What Is Vulnerability Management?
Vulnerability management is the continuous process of identifying, assessing, prioritizing, treating, and monitoring security weaknesses in an organization’s IT environment.
A vulnerability can exist in:
- Software and operating systems
- Servers and endpoints
- Cloud infrastructure
- Networks and applications
- Databases
- APIs
- Containers and Kubernetes environments
- IoT devices
- Network appliances
- Third-party components and dependencies
The goal is not simply to find vulnerabilities. It is to reduce security risk by making sure the most dangerous weaknesses are addressed first and continuously monitored.
Vulnerability Management Lifecycle
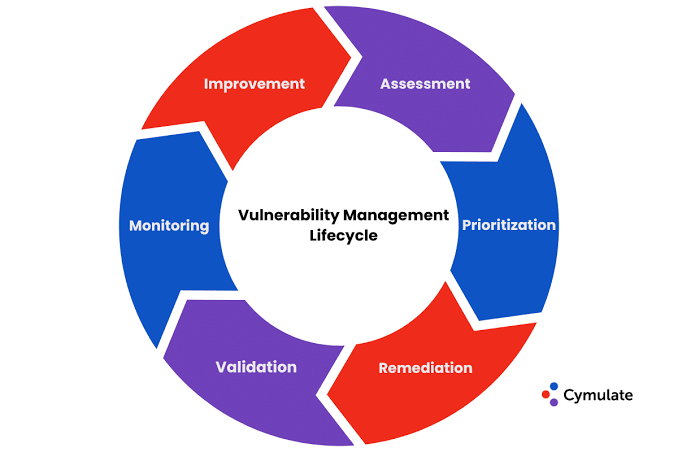
A typical vulnerability management program follows these stages:
1. Asset Discovery
Organizations first need to know what they own and operate.
Asset discovery can identify:
- Laptops and desktops
- Servers
- Virtual machines
- Cloud resources
- Applications
- Databases
- Network devices
- Containers
- APIs
- Mobile devices
- Internet-facing systems
An accurate asset inventory is important because an organization cannot effectively protect systems it does not know exist.
2. Vulnerability Identification
Security teams use vulnerability scanners and other security tools to identify weaknesses.
Common approaches include:
- Network vulnerability scanning
- Host-based scanning
- Web application scanning
- Cloud security assessments
- Container scanning
- Dependency scanning
- Configuration assessments
- Penetration testing
- Security code analysis
Vulnerability information can also come from sources such as vendor security advisories and the Common Vulnerabilities and Exposures (CVE) system.
3. Vulnerability Assessment
Finding a vulnerability does not automatically mean it represents a critical business risk.
Security teams assess factors such as:
- Severity
- Exploitability
- Asset importance
- Internet exposure
- Availability of exploits
- Existing security controls
- Business impact
- Data sensitivity
- Potential attack paths
4. Risk-Based Prioritization
Organizations usually cannot fix every vulnerability immediately.
They therefore prioritize vulnerabilities according to risk.
For example:
Critical priority
- Known active exploitation
- Internet-facing critical systems
- Vulnerabilities allowing remote code execution
- Systems containing highly sensitive information
High priority
- Easily exploitable vulnerabilities
- Important production systems
- Vulnerabilities with significant privilege escalation potential
Medium priority
- Limited exploitation potential
- Systems with compensating controls
Low priority
- Difficult-to-exploit weaknesses
- Low-impact systems
- Vulnerabilities with strong mitigating controls
5. Remediation
Remediation involves eliminating or reducing the vulnerability.
Common remediation actions include:
- Installing security patches
- Updating software
- Upgrading operating systems
- Removing unsupported software
- Changing insecure configurations
- Disabling unnecessary services
- Replacing vulnerable components
- Improving access controls
- Applying network segmentation
6. Validation
After remediation, security teams verify that the vulnerability has actually been resolved.
This can involve:
- Rescanning the system
- Checking the installed software version
- Testing the configuration
- Performing penetration testing
- Reviewing security logs
7. Continuous Monitoring
Vulnerability management is not a one-time project.
New vulnerabilities are discovered continuously, while organizations continuously add new:
- Applications
- Devices
- Cloud services
- Software dependencies
- Users
- Infrastructure
Therefore, organizations need ongoing vulnerability monitoring.
Vulnerability Management vs. Vulnerability Assessment
These terms are related but different.
| Vulnerability Assessment | Vulnerability Management |
| Identifies vulnerabilities | Manages vulnerabilities throughout their lifecycle |
| Often performed periodically | Continuous process |
| Focuses on discovery and analysis | Includes discovery, prioritization, remediation, and validation |
| Produces assessment results | Produces an ongoing risk-management process |
A vulnerability assessment can be considered one component of a broader vulnerability management program.
Common Vulnerability Scoring
One widely used framework is the Common Vulnerability Scoring System (CVSS).
CVSS provides a standardized way to describe the technical severity of vulnerabilities.
Factors can include:
- Attack vector
- Attack complexity
- Required privileges
- User interaction
- Scope
- Confidentiality impact
- Integrity impact
- Availability impact
However, a CVSS score should not necessarily determine remediation priority by itself.
For example, a high-CVSS vulnerability on an isolated test server may represent less immediate business risk than a moderately scored vulnerability affecting an internet-facing production application.
Exploitability and Threat Intelligence
Modern vulnerability management increasingly considers whether a vulnerability is actually being exploited.
Security teams may examine:
- Public exploit availability
- Exploit maturity
- Active exploitation reports
- Threat-intelligence feeds
- Attacker behavior
- Vulnerability age
- Exposure to the internet
This helps organizations move from simply asking:
“How severe is this vulnerability?”
to:
“How much risk does this vulnerability create for our organization right now?”
Vulnerability Management Tools
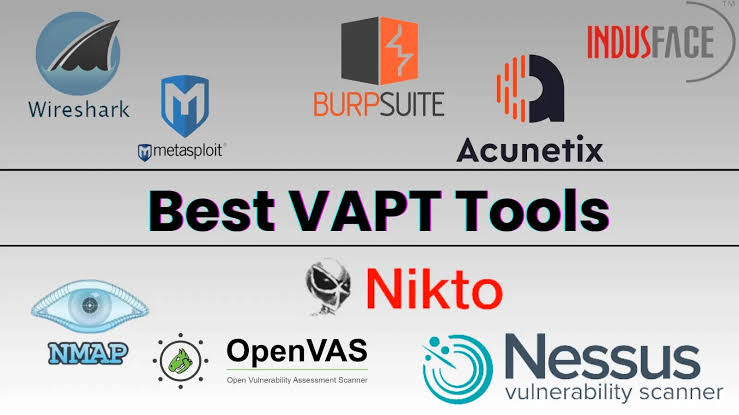
Organizations commonly combine several types of security technologies.
Vulnerability Scanners
Used to identify vulnerabilities across systems and networks.
Endpoint Security Platforms
Monitor endpoints and may identify vulnerable software.
Cloud Security Platforms
Identify vulnerabilities and misconfigurations in cloud environments.
Web Application Scanners
Search websites and web applications for security weaknesses.
Container Security Tools
Scan container images and dependencies for vulnerabilities.
Software Composition Analysis
Identifies vulnerabilities in third-party and open-source software dependencies.
Patch Management Platforms
Help organizations deploy software and security updates.
Security Information and Event Management
SIEM platforms can provide additional context from security events and logs.
Exposure Management Platforms
Broader exposure-management approaches combine vulnerabilities, assets, identities, misconfigurations, and attack paths to help organizations understand overall exposure.
Vulnerability Management in Cloud Computing
Cloud environments create additional challenges because infrastructure can change rapidly.
Organizations need to monitor:
- Virtual machines
- Containers
- Kubernetes clusters
- Cloud storage
- Databases
- APIs
- Identity and access configurations
- Serverless applications
- Infrastructure-as-code
- Cloud network configurations
Cloud vulnerability management should therefore be integrated into development and deployment processes rather than performed only after systems reach production.
Vulnerability Management and DevSecOps
Modern organizations increasingly integrate vulnerability management into the software development lifecycle.
A typical process might look like this:
Code → Build → Dependency Scan → Container Scan → Security Testing → Deployment → Continuous Monitoring
Developers can identify vulnerabilities before applications reach production.
This approach can reduce the cost and effort associated with fixing security problems later in the development lifecycle.
Vulnerability Management Best Practices
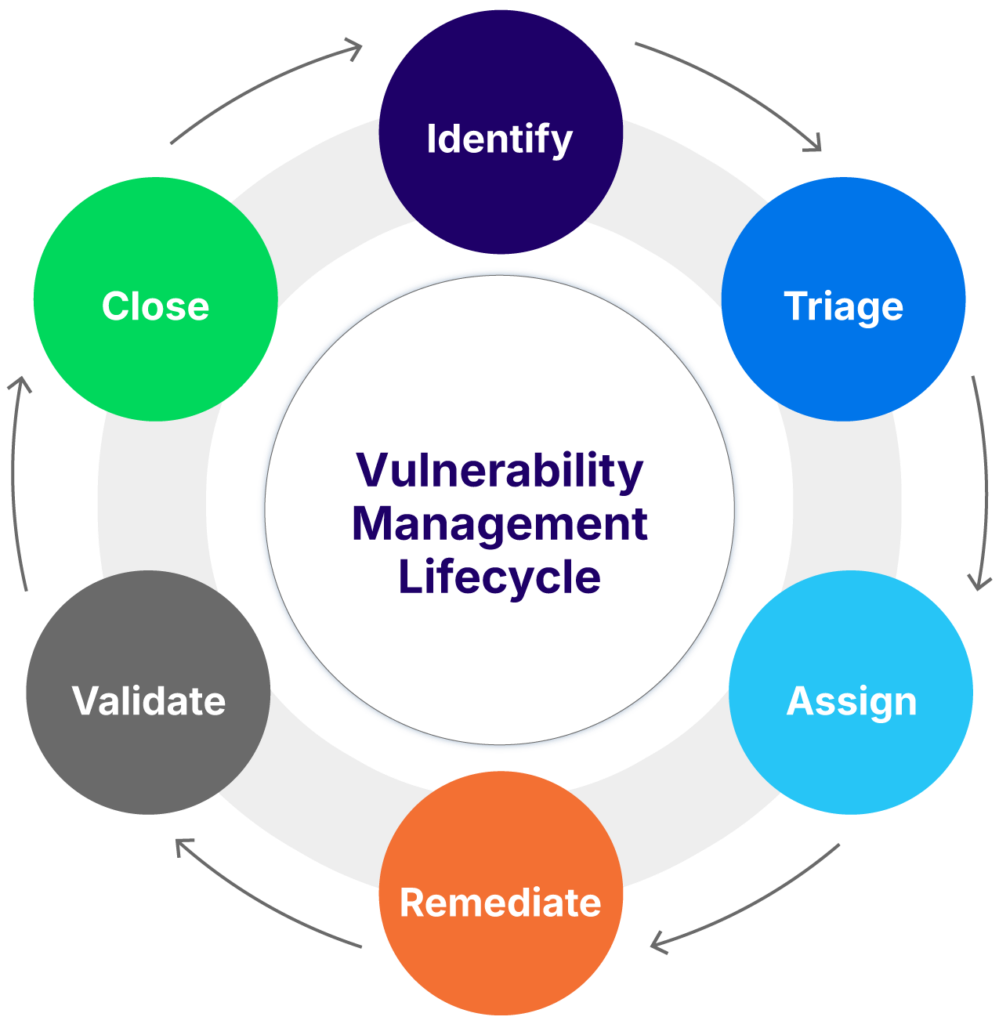
Maintain an Accurate Asset Inventory
You need visibility into hardware, software, cloud resources, applications, and services.
Prioritize Risk
Do not treat every vulnerability equally.
Consider:
Technical severity + exploitability + exposure + business impact
Patch Critical Vulnerabilities Quickly
Especially vulnerabilities affecting internet-facing or business-critical systems.
Automate Where Possible
Automation can help with:
- Asset discovery
- Vulnerability scanning
- Ticket creation
- Patch deployment
- Rescanning
- Reporting
Continuously Scan
Periodic scanning can miss newly introduced vulnerabilities.
Track Remediation
Every significant vulnerability should have:
- Owner
- Priority
- Due date
- Remediation status
- Validation status
Use Compensating Controls
When immediate patching is impossible, organizations may reduce risk through:
- Network segmentation
- Firewall rules
- Access restrictions
- Application controls
- Monitoring
- Service isolation
Measure Performance
Useful metrics include:
- Number of critical vulnerabilities
- Mean time to remediate
- Percentage of vulnerabilities remediated within SLA
- Vulnerability recurrence rate
- Asset coverage
- Patch compliance
- Number of internet-facing vulnerable assets
Vulnerability Management Challenges
Organizations often face:
- Incomplete asset inventories
- False positives
- Too many vulnerabilities
- Legacy systems
- Unsupported software
- Limited security resources
- Slow patching processes
- Cloud complexity
- Third-party dependencies
- Shadow IT
- Rapidly changing infrastructure
A mature vulnerability management program addresses these challenges through automation, prioritization, and strong ownership.
Vulnerability Management Framework
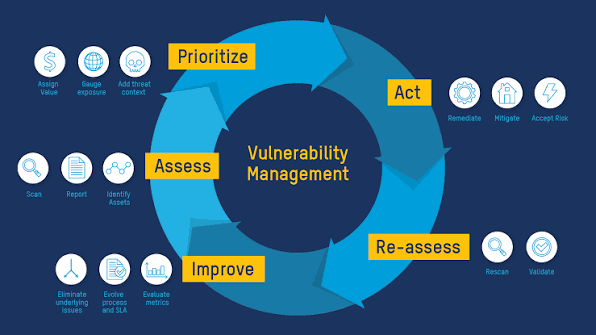
A practical framework can be summarized as
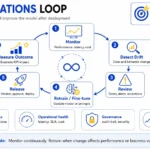
Discover → Scan → Assess → Prioritize → Remediate → Validate → Monitor → Report
This cycle repeats continuously.
Importance of Vulnerability Management
Effective vulnerability management helps organizations:
- Reduce attack surfaces
- Reduce the likelihood of successful exploitation
- Protect sensitive data
- Improve regulatory compliance
- Reduce security incidents
- Improve patch management
- Strengthen cloud security
- Improve visibility across IT environments
- Support broader cybersecurity risk management
Conclusion
Vulnerability management is a continuous cybersecurity discipline rather than a simple vulnerability-scanning activity. Its effectiveness depends on maintaining accurate asset visibility, identifying vulnerabilities, understanding their real-world risk, prioritizing remediation, validating fixes, and continuously monitoring the environment. A risk-based and increasingly automated approach allows organizations to focus limited security resources on the vulnerabilities that matter